DOING BUSINESS SIMPLIFIED – CLAIMING FORCE MAJEURE DUE TO BUSINESS DISRUPTIONS FROM COVID-19


As our leaders, health workers and we all continue to battle the spread of Covid-19 worldwide, we are aware that businesses are also battling the effects of Covid-19 on their operations. A lot of  industries have been hit due to lockdowns, travel bans, closed ports, amongst other government measures put in place.

A major question arising amongst businesses struggling to meet contractual obligations, is whether or not they can rely on the Force majeure clauses in their contracts to gain relief from performance of their existing contractual obligations due to Covid-19 pandemic.

If you are affected in this manner, we have set out below some useful information on Force Majeure to guide your next steps in this regard.

What is a Force Majeure clause?

A  Force Majeure clause is a contractual term which enables a party cancel or suspend or delay performance of an obligation under a contract as a result of an event beyond their control. Force Majeure events include an act of God, war or military operations, outbreak of diseases, acts of government, change of government laws and policies, etc.

What must I do to claim Force Majeure as a result of Covid-19?

  • Confirm existence of Force Majeure Clause– The first step is to confirm that there is a Force Majeure clause in your contract.


  • Confirm the event qualifies as a Force Majeure event: It is necessary to review the  Force Majeure clause to confirm that the particular reason for your delay or inability to perform is within the definition of the Force Majeure Event.  For instance, where your failure to perform is directly caused by Covid-19, you may be in a position to claim “Pandemic”  or “Epidemic” as the Force Majeure Event. If it is as a result of measures put in place by government to battle the spread of the virus, it may fit into “Act of Government”.


If you are uncertain as to if the reason for the delay falls within the definition of Force Majeure Events in your contract, it is advisable you seek legal assistance.


  • Show that the Force Majeure Event is beyond your control:  You must also show that the event was beyond your control (unless your contract does not require you to prove this).


  • Show causation: You are also required to show that your inability to perform is directly attributable to the Force Majeure Event i.e.you were prevented, delayed or hindered by reason of the Force Majeure event from performing your duty under the contract.


  • Show you took steps to mitigate effect: You must also show that you took steps to avoid the effect of the Force Majeure event but these steps were to no avail; or that there were no reasonable steps that you could have taken to avoid or mitigate the Force Majeure event and its consequences on your ability to perform.

I think I have a case for Force Majeure. What steps should I adopt now?

If you are clear that you have a right to claim Force Majeure, you must follow the requirements of the Force Majeure clause in your contract (as guided by your lawyers) in order to successfully rely on it.

Your contract would typically require you to adopt the following steps:

  1. Notification of the other party: Immediately notify the party of the occurrence of the Force Majeure event and describe, at a reasonable level of detail, the circumstances causing such delay or inability to continue the performance of the contract.


  1. Reasonable efforts: Use reasonable efforts to perform (or recommence performing) your obligations including through the use of alternative sources and workarounds, where possible.


  1. Notification of Cessation of Force majeure Event. Upon cessation of circumstances leading to the Force Majeure event, notify the other party of such cessation and resume performance as agreed with that party.

When can I terminate the Contract based on Force Majeure?

The terms of your contract would clearly state the period of time the Force Majeure event should have continued for before you are permitted to terminate. For instance, it may state that “where the Force Majeure event continues for a long period e.g. thirty (30) days or more depending on the contract, either of the parties may terminate the contract upon giving notice of such termination to the other party”.

Conclusion

It is important to understand that Force Majeure clauses do not automatically relieve businesses of their obligations under contracts including in the current Covid-19 situation. In order to confirm you can rely on the Force Majeure provisions in your contract, the clause must be carefully reviewed by you or your lawyer to confirm that your reason for your non-performance meets the requirements of the Force Majeure clause.
The Place of Data Protection in Nigeria amidst the Global Pandemic

The world is faced with one of the most serious global health security threats in decades – COVID-19. As we struggle to seek remedies, companies, organisations and governments have begun to make decisions to restructure their processes to fight against its continuous spread.

Amidst these mitigating measures, the need for compliance with privacy laws have never been more crucial. In Nigeria for instance, many of these measures involve the collecting and processing of personal information of Nigerian Citizens including sensitive information (such as health data). Data Privacy regulations seek to compliment rather than hinder the management of public health for the purpose of fostering openness of affected patients.

Companies, health care givers, journalists and governmental organisations who are concerned with implementing those mitigating steps (“Data Controllers”), should consider the following as they implement their safeguards to curb the spread of COVID-19 within Nigeria:

Collecting and Processing

At the point of collection of personal information, the consent of the individual (‘Data Subject”) should be obtained. However, the Nigeria Data Protection Regulation (NDPR) permits that where consent cannot be obtained, the data may be collected where there is a legal obligation to do so or in the interest of the general public.

In other words, to lawfully process the data obtained from a Data Subject, the Data Subject should have consented to the processing. However, where the Data Subject restricts processing of his data, the NDPR permits that the data be processed for the purpose of “public interest” in Nigeria. In addition, the Data Controller is expected to adopt a transparency policy by disclosing to the Data Subjects, the purpose of obtaining their data  and details of all third parties who will be processing the information. Only data which is necessary for the purpose of achieving   the objective should be collected and processed.

Confidentiality

Information such as name, age and gender collected by the Data Controller are to be protected. The NDPR places an obligation on the Data Controller to maintain the confidentiality of the information acquired and to minimize the access to the data. Thus, hospitals and employers of patients for example, should refrain from disclosing the identities of patients to third parties without their consent.

Accountability

Where any Data Controller is negligent which leads to a data breach, the Data Controller who obtained the information from the Data Subject, shall be accountable to the Data Subject. Where the Data Subject suffers any form of damage, he may bring an action and complaint against the Data Controller both in the court of law and before the National Information Technology Development Agency (NITDA).  Therefore, Hospitals, government agencies and employers in the context of dealing with information of patients, have a duty to be accountable to them, in the event of a data breach.

Erasure

The data obtained by the Data Controller must not be kept longer than required. The information is expected to be properly discarded once processing has been completed and  where it is no longer necessary to continue to store that data.

Conclusion

There is a need to create a balance between public interest and privacy rights of individuals for the effective combat of COVID-19 and other diseases. Amidst health risks, the NDPR remains operational to ensure the protection of the privacy of everyone affected.


Pavestones Regulatory Update: The Draft Revised Guidelines for the Regulation and Supervision of Microfinance Banks

The Central Bank of Nigeria (CBN) on March 3, released its revised Microfinance Bank (MFB) draft guidelines (the “Draft Revised Guidelines”). The Draft Revised Guidelines revises the increase in the minimum share capital for MFBs which was previously announced by the CBN in a notice released in October 2018; and expands the categories of MFBs, amongst other changes.

Although the guidelines are still in draft form, it is useful for MFBs and fintechs (who utilize MFB licenses) to take note of the changes proposed whilst assessing how it will affect their operations once it takes effect.

We have set out below, the major changes made to the Draft Revised Guidelines and how it differs from the Guidelines issued in 2012 (“2012 Guidelines”).

1.Categories of MFBs

Under the 2012 Guidelines, the CBN split MFBs into 3 (three) categories namely Unit MFBs, State MFBs, and National MFBs. The Draft Revised Guidelines splits the Unit MFBs to Tier 1 and Tier 2. This brings the categories of MFBs to 4 (four) namely: Tier 1 Unit MFBs; Tier 2 Unit MFBs; State MFBs, and National MFBs.

The benefit of this revision is that Unit MFBs would no longer be restricted to one location. Tier 1 Unit MFBs would be permitted to operate in urban areas and have up to 4 (four) branches in addition to the head office, within 5 (five) Local Governments Areas (LGA) in the state. Tier 2 Unit MFBs would be permitted to have a head office and a branch within the same LGA. Note that Tier 2 MFBs are to operate in rural and unbanked/underbanked areas.

It is also useful to note that the number of branches State and National MFBs may establish at commencement is capped at 10 under the Draft Revised Guidelines. In the 2012 Guidelines, this is not capped.

2.Financial Requirements

The capitalization requirement for each category of MFB in the Draft Revised Guidelines are as follows: Tier 1 Unit – 200 million Naira; Tier 2 Unit – 50 million Naira; State MFBs – 1 billion Naira; and National MFBs – 5 billion Naira.

With this revision, MFBs would have the option to apply for a Tier 2 Unit MFB license with a share capital requirement of 50 million Naira as opposed to the 200 million Naira minimum capital requirement for Unit MFBs stated in the MFB capitalization review notice earlier issued in October 2018.

3. Licensing Requirements.

Under the Draft Revised Guidelines, promoters and investors of MFBs  would be required to make presentations on the business case of the proposed MFBs before a formal application for an MFB licence. The CBN will also inspect the premises and facilities of MFBs prior to granting a final licence.

Conclusion

The tiered Unit MFB license would be a welcome development as it has the potential to include MFBs who are unable to meet the current 200 million Naira capital requirement. It would also allow MFBs reach more customers with the introduction of branches.

Notwithstanding this, it would be useful to see regulations that are tailored to the peculiar structure of digital banks and fintech businesses, as the regulation of this space is still subject to multiple interpretation by regulators of the available laws/regulations.

CONSUMER PROTECTION IN NIGERIA

On the 28th of February 2020, Social Media was abuzz with reports from a distressed user about the hike in the price of hand sanitizers, at over 300% of the original price, in the wake of the Corona Virus epidemic which a patient was recently diagnosed with in Nigeria. The Federal Competition and Consumer Protection Commission (the “Commission”) is the agency responsible for safeguarding the rights of consumers as empowered by the Federal Competition and Consumer Protection Act, 2019 (“FCCPA”).

The Director General of the Commission, Mr. Babatunde Irukera, through a press statement, condemned the actions of retailers who were accused of price gouging and taking advantage of the desperation of Nigerians in finding measures to curtail the virus. He immediately took steps to put an end to this arbitrary increase in prices, thereby creating awareness in the minds of unknowing consumers about the protection accorded them and the recourses available in the event of an infraction.

SCOPE OF THE FCCPA

Generally, the FCCPA aims to promote and secure a competitive market in Nigeria, endorsing efficiency in the economy and disallowing restrictive and unfair business practices.

HOW ARE CONSUMERS PROTECTED?

Under the FCCPA, rights of consumers are clearly spelt out. A few of these rights are highlighted below;

Due Consideration of consumers’ interests

Where retailers engage in obnoxious practices or the exploitation of consumers, the Commission has the responsibility of ensuring that complaints received from consumers are provided adequate attention and redress. In other words, as in cases of arbitrary price hikes, it is the duty of the Commission to investigate and provide remedies for complainants.

Right to disclosure of price of goods or services

Specifically, the FCCPA requires that the price of goods or products and services must be distinctly and clearly stated (by manufacturers, distributors or retailers) in a position where consumers can easily identify them.  Prices must be displayed in the currency of Nigeria (N) in a conspicuous location close to the product or in a brochure or catalogue available to the consumer.

Product labelling and descriptions

Products must be accurately labelled and described to the consumers ensuring they are not misled. Product labelling refers to any written description about the product which is either placed close to the product, any advertisement made in connection to the product and any label attached to the product.


CONCLUSION

Suppliers, Producers and Manufacturers must take note of consumers’ rights under the FCCPA so that they are aware of their compliance requirements under the FCCPA and the possibility of being sanctioned where they are found to be in breach.


Data Driven Marketing; How far is too far?

The world is currently in an era termed the “Experience Economy”. Joseph Pine II and James H. Gilmore in their 1998 Harvard article described the world’s economic progress in the following terms:

Agrarian economy –>

i.e. consumers purchased farm products directly

Industrial economy –>

i.e. consumers purchased processed products. —->

Service economy –>

i.e.  consumers relied on service providers. —->

Experience economy

i.e. consumers now seek memorable/personalised experiences.


To attract and retain customers in today’s “Experience Economy”, businesses must now consider ways to provide personalised services/memorable experiences to its customers. This can be done by gathering insights from data to better understand the customers’ needs. These insights are then adopted to offer the customers, product tailored to their needs (Data Driven Marketing).

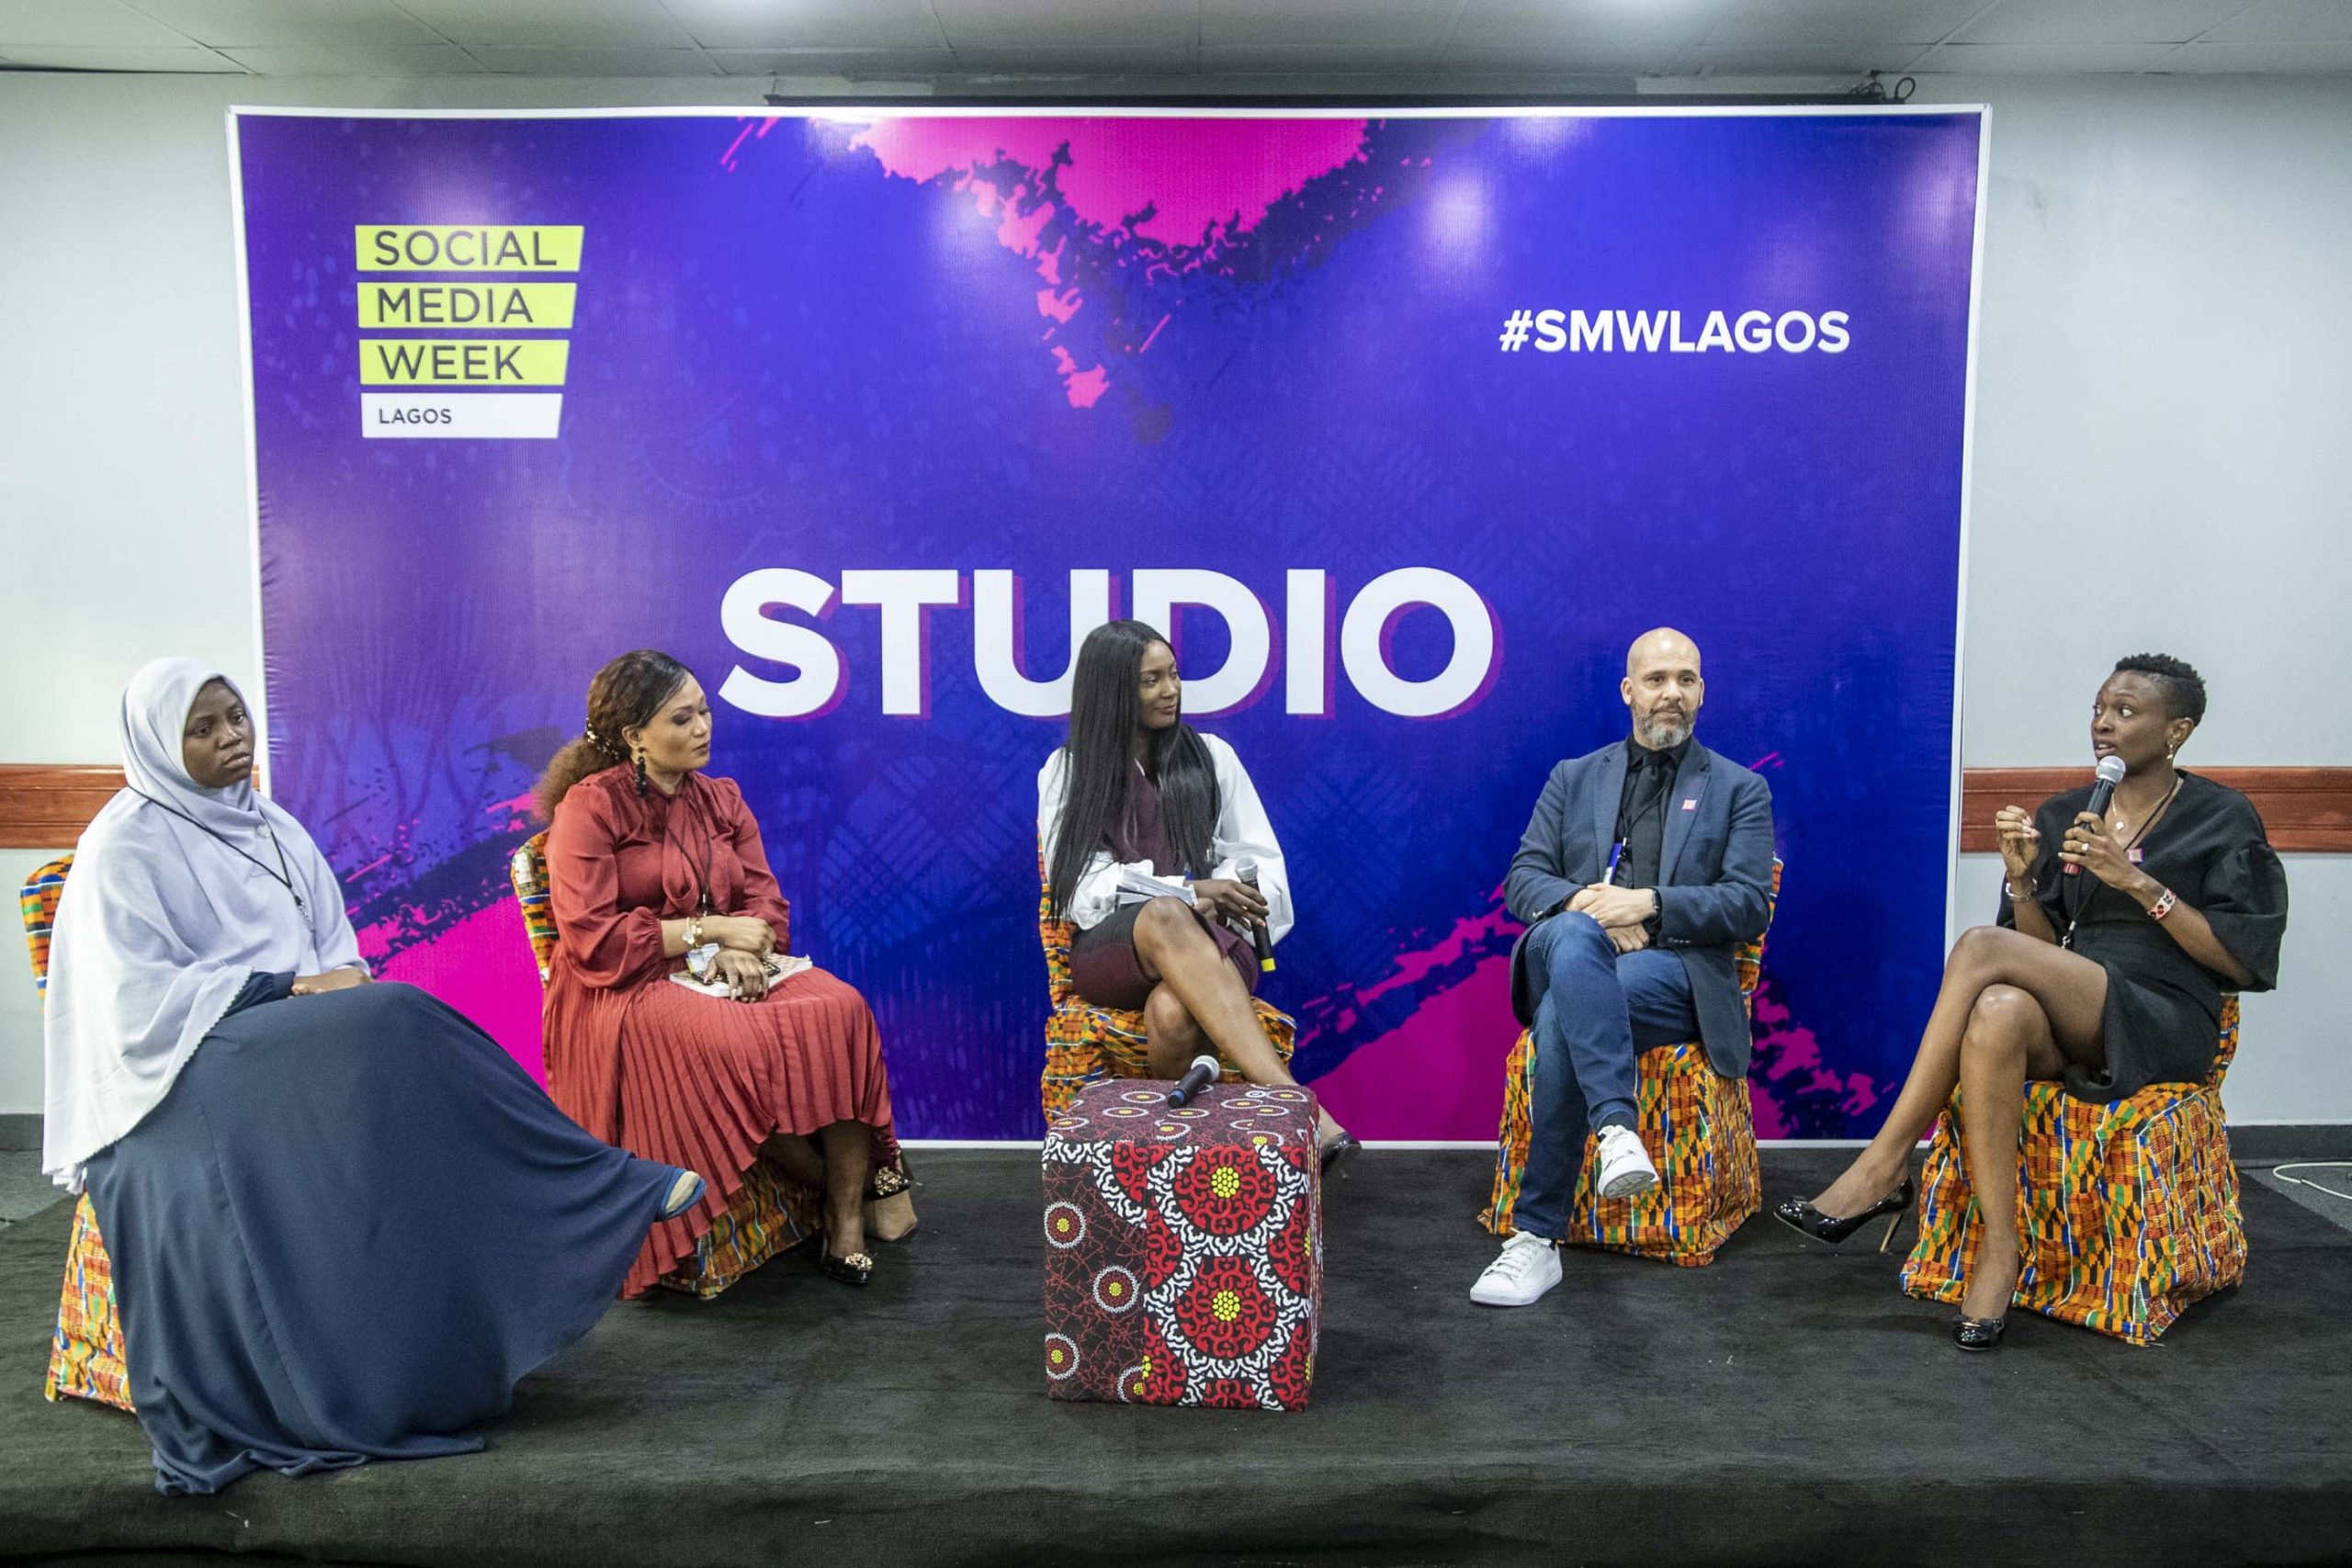
At our Social Media Week session titled: “Eye-spy; how far is too far?,” we discussed Data Driven Marketing within the confines of the law.  Our panellists provided valuable insights on the positive aspects of data driven marketing and the strategy to adopt to successfully carry out this form of marketing. We also discussed how far would be considered as too far in utilising the data of people (particularly in the context of the Nigeria Data Protection Regulation) and agreed that data must be used responsibly to avoid infringing on the privacy of users.

Here are certain points your business should note from the Nigeria Data Protection Regulation (NDPR) as you develop your own Data Driven Strategy:

  1. obtain the consent of the consumers (Data Subjects) before collecting data;
  2. collect only data required by your business whilst ensuring that the data is stored in a safe place;
  3. before data can be transferred to any third party, the Data Subject must consent to the transfer (this can be done with a properly drafted and accepted privacy policy);
  4. display a simple and easy-to-understand privacy policy that states, amongst other things, the remedies available to the Data Subject in the event of a breach;
  5. appoint a Data Protection Officer (DPO) (within your organisation or outsourced) who will ensure that that the company complies with all data protection regulations;
  6. where you process personal data of 1000 data subjects within a period of 6months, you are required to submit to a desktop audit by a Data Protection Compliance Organization licensed by National Information Technology Development Agency (NITDA); and
  7. where you process personal data of over 2000 data subjects in a period of 12 months, you are required to file reports with NITDA by March 15 yearly.

For more information on the foregoing, contact us at info@pavestoneslegal.com